For years, cybersecurity professionals have told people to avoid suspicious websites.
Don't click strange links. Don't download files from sketchy sources. Don't enter your credit card number on a website that looks like it was built in someone's basement in 2004.
Perfectly reasonable advice.
But what happens when the malicious code arrives through a website you recognize?
What happens when you visit a legitimate news outlet, software company, or major retailer, and the problem isn't the website's reputation?
Welcome to the wonderful world of software supply-chain attacks, where your favorite website can be perfectly respectable and still serve something it shouldn't.
What Happened on November 16?
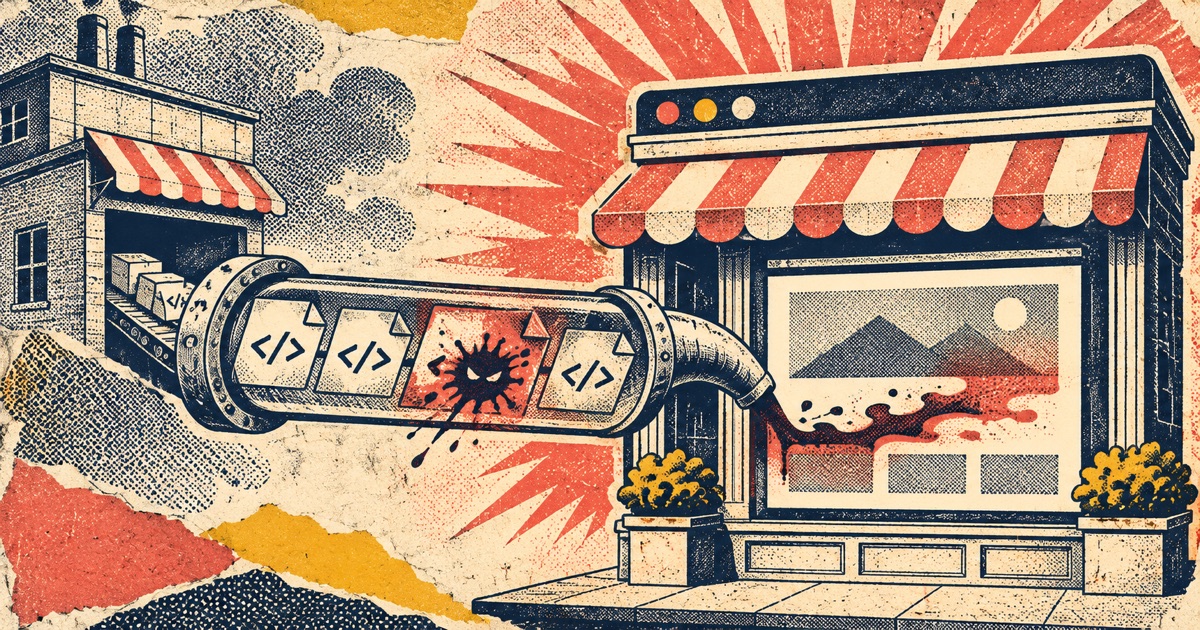
On November 16, 2026, security researcher Scott Helme and the team at Report URI identified malicious JavaScript being delivered through Optimizely, a platform that organizations use to experiment with, personalize, and improve their websites.
Optimizely's technology is embedded in websites to support features like A/B testing.
For anyone unfamiliar with A/B testing, it's the process of showing different visitors different versions of a page to determine which one performs better.
Perhaps one button says “Get Started” and another says “Start Now.”
Marketing teams can spend weeks analyzing which one gets clicked more often.
Meanwhile, a criminal found a way to turn some of that same delivery infrastructure into a malicious-code distribution channel.
Researchers examined 1,611 Optimizely JavaScript snippets and identified 188 infected snippets associated with 178 organizations.
That does not mean attackers breached 178 separate corporate networks. Some entries were regional sites, specialized services, or development environments. The finding concerns the Optimizely snippets associated with those organizations, not every page on every named website.
The identified organizations included major names such as Zoom, BBC, CNN, Salesforce, GitLab, IKEA, and others.
That's not a list of obscure websites with suspicious URLs and animated skulls.
These are recognizable organizations that people visit for legitimate reasons.
In its November 17 incident report, Optimizely said an unauthorized party exploited a flaw in the Web Experimentation account-signup flow, impersonated authorized users, and inserted malicious JavaScript into customer projects.
The company reported that it fixed the vulnerability and removed the injected code. Its incident history says the incident was limited to Web Experimentation and affected less than 5% of its customers.
What Was the Malicious Code Trying to Do?
This wasn't just a script displaying annoying pop-up advertisements.
The payload analyzed by Report URI was capable of several harmful actions:
Cryptocurrency theft. It could replace a legitimate cryptocurrency wallet address with one controlled by an attacker.
Imagine copying an address to send money, pasting it, and unknowingly sending the funds somewhere else.
Crypto transactions are generally difficult or impossible to reverse. That's why checking the destination matters.
Payment-card skimming. The code could capture payment information entered into certain website-controlled forms.
Not all payment forms were equally exposed. Researchers found that some isolated third-party payment fields were protected from the script's reach.
Browser-data theft. The malicious code could access certain cookies and capture screenshots.
Report URI found this collection was tied to conditions involving cryptocurrency-address replacement; it did not establish that every visitor's cookies or screenshots were taken.
Mobile-device exploitation. Researchers also identified attempts to direct vulnerable iPhones and iPads toward exploit kits targeting older software.
That last point is particularly important.
A website attack is not always just about persuading someone to type in a password. Sometimes attackers target vulnerabilities in the software used to visit the site.
Researchers identified cryptocurrency transactions to wallets associated with the attack. The exact amount stolen during this campaign is difficult to establish because some wallets had activity before it.
What we don't yet know is the full extent of stolen payment information, affected individuals, or any successful device compromises.
And no, identifying malicious code on an organization's website does not mean that every visitor was infected or had information stolen.
CyberGuy's consumer-focused report also covers the affected-site inventory and the mobile-device risk. Apple told CyberGuy that the underlying vulnerabilities had been patched; that is another reason to install the latest security update available for your device. A detected exploit attempt is not proof that this campaign successfully compromised an iPhone or iPad.
Why This Attack Matters More Than the Brand Names
The underlying problem is one of trust.
Modern websites rarely consist entirely of code written and controlled by the organization whose name appears at the top.
They rely on outside vendors for analytics, advertising, customer support, payments, personalization, and countless other functions.
Each integration can provide useful capabilities.
It can also introduce additional risk.
Think of a website as a restaurant.
You may know and trust the restaurant. The kitchen looks clean. The employees are professional.
But the restaurant still depends on suppliers.
If a supplier delivers contaminated ingredients, the restaurant's reputation doesn't magically make the ingredients safe.
The Optimizely incident is a digital version of that problem.
Organizations trusted the service delivering the code. Visitors trusted the organizations displaying it.
The attackers exploited that chain of trust.
And this is why HTTPS and the little padlock icon are not guarantees that a website is harmless.
HTTPS helps protect the connection between you and a website. It doesn't certify that every script the website loads is safe.
Your browser can have a perfectly secure connection to something malicious.
Technology is full of wonderful little ironies like that.
What Should Ordinary People Do?
First, let's avoid declaring a nationwide credit-card emergency.
There's no evidence that everyone who visited one of the named websites had their payment details stolen.
Risk depends on which page was visited, when it was visited, what code loaded, the device involved, and what the user did.
But there are sensible steps everyone can take.
1. Update your devices and browsers
Install current security updates on your phone, tablet, computer, and browser.
This is especially important when researchers identify exploit attempts targeting older operating-system versions.
Security updates aren't merely opportunities for your phone to rearrange the settings menu again. Sometimes they close vulnerabilities that criminals are actively trying to exploit.
2. Monitor payment accounts
If you entered payment-card information directly into a website during the affected period, review the transaction history for that card.
Enable transaction alerts where available.
If you discover an unauthorized charge, contact your card issuer immediately using its official number or app.
You do not need to cancel every payment card you own just because a familiar company appeared in a security report.
3. Double-check cryptocurrency destinations
Before sending cryptocurrency, verify the entire destination address using a trusted source.
Don't assume the address in your clipboard is the one you copied.
If you use cryptocurrency regularly, consider hardware-based transaction verification and other controls supported by your wallet.
4. Pay attention to unusual account activity
Unexpected sign-ins, security notifications, password-reset messages, or unexplained account changes deserve investigation.
Use the service's official website or app to check.
Do not follow an unexpected “your account may have been compromised” link, especially when there's a major security incident in the news.
Yes, scammers exploit the news about other scammers.
It's scammers all the way down.
If you receive a follow-up message claiming you need to verify your account or install a security tool because of this incident, open the organization's real site yourself. ZoraSafe's Ask Zora can help you assess suspicious messages and scam warning signs. It cannot detect malicious website JavaScript or certify that a device is free of malware.
5. Don't confuse consumer responsibility with corporate responsibility
Consumers should update software and monitor accounts.
But the real burden of preventing malicious third-party scripts belongs to the organizations and technology providers deploying them.
Website operators should monitor externally loaded code, restrict what third-party scripts can access, use strong content security policies where appropriate, and investigate suspicious changes.
It's unreasonable to expect an ordinary consumer to inspect JavaScript before buying a sweater.
The Bigger Lesson
The Optimizely incident illustrates something cybersecurity education needs to acknowledge more openly.
Sometimes people do everything we've told them to do, and the technology still exposes them to risk.
That's not an argument for giving up.
It's an argument for better vendor security, stronger browser protections, faster vulnerability remediation, and consumer guidance that reflects how modern attacks actually work.
Keep your devices updated. Monitor accounts. Verify payments.
But also demand accountability from the companies building and operating the services you rely on.
Because “don't visit sketchy websites” is no longer a complete cybersecurity strategy.
Sometimes the website is legitimate.
The problem came through the front door wearing a vendor badge.
Sources
- CyberGuy — Hackers turn trusted websites into malware traps
- Report URI — Scott Helme's November 16, 2026 investigation
- Optimizely — November 17 security incident report
- Optimizely — Official incident history
- BleepingComputer — Optimizely supply-chain incident reporting